As boards race to embed AI across the enterprise, new data shows most security leaders doubt their ability to contain AI-driven incidents without disruption.
Dark web service Nexus is selling 153M+ driver’s license scans allegedly stolen from IDScan.net, prompting an FBI probe and alarms over age‑verification data.[1]
US and European authorities, working with CrowdStrike and Shadowserver, have disrupted the 23-year-old Sality P2P botnet, severing its malware delivery channels.
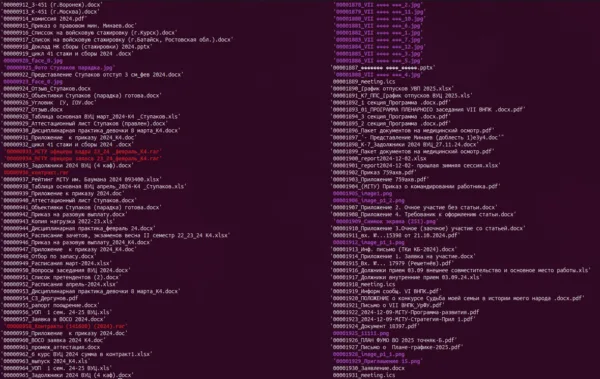
Leak from Bauman University’s secret Department No. 4 reveals a GRU-directed cyber-operator pipeline feeding units like APT28 and Sandworm, reshaping threat models.
Attackers abused a misconfigured METR agent dashboard to steal an API key, running up about $600K in AI model credits before the nonprofit cut off access.
A federal whistleblower warns USPS’s rushed ballot mail IT systems under Trump’s new rule could reject valid mail-in ballots and trigger legal fights in 2026.
A new ClickFix campaign chains fake fixes with EtherHiding C2 on the Polygon blockchain, evading takedowns while quietly infecting unwitting organizations.
White House and Texas leaders launched Project Watershed 250, a six-month pilot delivering free cyber defense to under-resourced water utilities statewide.